CyberForce 2024 Adventure Writeup
Solutions to Department of Energy CyberForce Adventure 2024 anomalies: browser-history forensics, WAF log analysis, steganography, C++ reversing, phishing triage, and trivia.
Contents
- Securely Provision
- Anomaly 74-76: Tears of the Analyst-C++ Class Reversing
- Protect and Defend
- Anomaly 21-25: TPS Report
- Anomaly 26-28: Nice Day for Phishing
- Anomaly 30: Trivia 02
- Anomaly 31: Trivia 03
- Anomaly 32: Trivia 04
- Anomaly 33: Trivia 05
- Anomaly 34: Trivia 06
- Anomaly 35: Trivia 07
- Anomaly 36: Trivia 08
- Anomaly 37: Trivia 09
- Anomaly 38: Trivia 10
- Anomaly 43: Trivia 15
- Anomaly 44: Trivia 16
- Anomaly 45: Trivia 17
- Anomaly 46: Trivia 18
- Anomaly 47: Trivia 19
- Analyze
- Anomaly 05-11: gURLs Just Want to Have Fun
- Anomaly 12-15: While My WAF Gently Weeps
- Anomaly 17: Ste-what-graphy v2
- Oversee and Govern
- Anomaly 29: Trivia 01
- Anomaly 16: COn365nt is Key
- Energy
- Anomaly 39: Trivia 11
- Anomaly 40: Trivia 12
- Anomaly 41: Trivia 13
- Anomaly 42: Trivia 14
- Anomaly 48: Trivia 20
- Investigate
- Anomaly 49: Knock Knock…Who’s There?
- Anomaly 50: Sloggin through these logins
These are my solutions to the Department of Energy's CyberForce Adventure 2024 anomalies, grouped by the competition's categories. For the multiple-choice trivia, the correct answer is in bold.
Securely Provision#
Anomaly 74-76: Tears of the Analyst-C++ Class Reversing#
Anomaly 74#
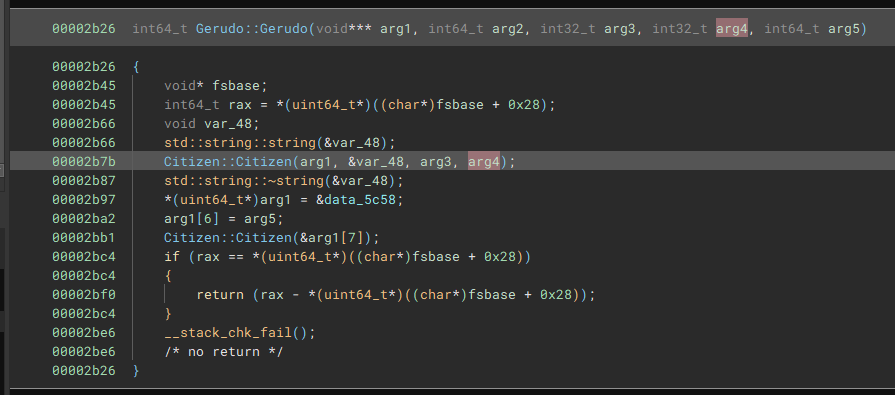
We can see that we are inheriting stuff from Citizen
Anomaly 75#
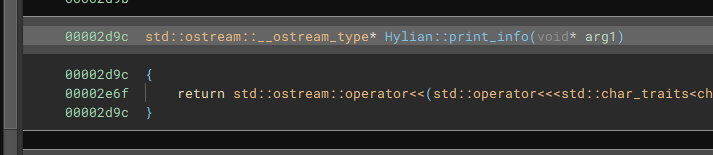
Looking at all the functions we see that this function is inherited
Anomaly 76#
We can see we are passing a string and two ints into the Citizen class
Protect and Defend#
Anomaly 21-25: TPS Report#
Anomaly 21#
Since we were not able to access it for a very long time and that the server just stored data we can mark it 6 Denial of Non-Critical Services
Anomaly 22#
Since no data was taken we give it 1 No Impact
Anomaly 23#
Since this was a public server it falls into cat 2 Business Network
Anomaly 24#
Since they were not able to access it then Availability was targeted
Anomaly 25#
We got to do some math and subtracting them 1715134320 - 1715128980 / 60 gives us 89
Anomaly 26-28: Nice Day for Phishing#
Ticket 1#
Spam, does not seem to try to impersonate, clone, etc.
Ticket 2#
First the from email stands out as very odd. But since it is targeting a high value individual it is whaling.
Ticket 3#
Since this is a text, this is smishing.
Anomaly 30: Trivia 02#
What is the primary purpose of a bind shell payload in a penetration testing scenario?
- a) To establish a reverse connection from the attacker's machine to the target system. - That is a reverse shell
- b) To execute arbitrary commands on the target system and return the results to the attacker. - Not the best answer
- c) To open a network port on the target system and listen for incoming connections from the attacker.
- d) To encrypt communication between the attacker and the target system to evade detection. - Not its goal
Anomaly 31: Trivia 03#
Explain the difference between symmetric and asymmetric encryption
- a) Symmetric encryption uses two different keys for encryption and decryption, while asymmetric encryption uses the same key for both processes.
- b) Symmetric encryption is faster than asymmetric encryption, while asymmetric encryption offers better security.
- c) Symmetric encryption uses a pair of keys: a public key for encryption and a private key for decryption, while asymmetric encryption uses only one key for both processes.
- d) Symmetric encryption uses a single key for both encryption and decryption, while asymmetric encryption uses a pair of keys: a public key for encryption and a private key for decryption.
Anomaly 32: Trivia 04#
Which of the following is a technique often utilized by attackers to evade detection by security tools and defenders, involving the encryption of malicious payloads to bypass signature-based detection mechanisms?
- a) Cross-site scripting (XSS) - This is an attack not an evasion mechanism
- b) DNS tunneling - This is a method of exfiltration but can be viewed and stopped
- c) Data exfiltration - This is just a term and not a method
- d) Payload obfuscation
Anomaly 33: Trivia 05#
In a penetration testing scenario, which of the following methods is commonly used to escalate privileges on a compromised system when traditional methods fail?
- a) Reverse engineering - Used to analyse malware
- b) Fuzzing - This is most commonly used to find flaws in a system
- c) Kernel exploitation
- d) DLL injection - While possible not that common
Anomaly 34: Trivia 06#
Which of the following is a technique used in a buffer overflow attack to redirect the program's execution flow to malicious code injected by the attacker?
- a) Code obfuscation - Not a bin attack
- b) Integer overflow - This just makes a number negative or positive, not touching control flow
- c) Return-oriented programming (ROP) - We are trying to overwrite the return address
- d) Cross-site scripting (XSS) - Not a bin attack
Anomaly 35: Trivia 07#
During a penetration test, the tester discovers an outdated FTP server running on the target network. Which of the following techniques would be MOST effective for exploiting this vulnerability?
- a) Directory traversal attack - Deals with paths
- b) Cross-site scripting (XSS) - Most common on websites
- c) SQL injection - Common on databases
- d) Buffer overflow exploit - Good if we have a function we are trying to access
Anomaly 36: Trivia 08#
In a penetration testing scenario, what is the primary purpose of using a reverse shell payload?
- a) To establish a connection from the attacker's machine to the victim's machine. - This is the definition of the attack
- b) To encrypt data transmitted between the attacker and the victim.
- c) To exploit a vulnerability in a web application.
- d) To perform a denial-of-service (DoS) attack on the target network.
Anomaly 37: Trivia 09#
In a penetration testing scenario, what is the primary objective of post-exploitation activities after gaining initial access to a target system?
- a) Deleting system logs to cover tracks - Not something we should do in a pentest we don't want to destroy our customer's network
- b) Extracting sensitive data from the compromised system
- c) Installing backdoors for persistent access - Not really needed in a pentest
- d) Patching vulnerabilities to secure the system - That is not our job we need to find vulns
Anomaly 38: Trivia 10#
In a penetration test, which of the following techniques would be most effective for escalating privileges after gaining initial access to a target system?
- a) Conducting a brute-force attack against system services. - Not the easiest way to get priv esc
- b) Exploiting misconfigured network shares to gain access to sensitive files. - We are not after files
- c) Leveraging a zero-day vulnerability to execute arbitrary code. - Rarely would you even know of a zero day or even use one, especially as a pen tester
- d) Exploiting a known vulnerability to escalate privileges via a privilege escalation exploit.
Anomaly 43: Trivia 15#
Which of the following is a key component of a firewall?
- a) Intrusion Detection System (IDS)
- b) Anti-virus software
- c) Router
- d) Access Control List (ACL) - Controlling access is their primary job
Anomaly 44: Trivia 16#
What is the main advantage of using asymmetric encryption over symmetric encryption?
- a) Faster encryption and decryption speed - Not true
- b) Requires only one key for both encryption and decryption - Not true
- c) Provides better security for key distribution - Breaks up keys
- d) Less complex implementation
Anomaly 45: Trivia 17#
What type of attack attempts to deceive users into visiting malicious websites by redirecting them from legitimate websites?
- a) Man-in-the-Middle (MitM)
- b) Cross-Site Scripting (XSS)
- c) Phishing
- d) SQL Injection
Anomaly 46: Trivia 18#
What is the purpose of a VPN (Virtual Private Network)?
- a) To hide IP addresses
- b) To secure network traffic over public networks
- c) To encrypt files on a local computer
- d) To prevent malware infections
Anomaly 47: Trivia 19#
Which of the following is NOT a common authentication factor?
- a) Password
- b) Biometrics
- c) Security Token
- d) Public Key - Usually a private key
Analyze#
Anomaly 05-11: gURLs Just Want to Have Fun#
Part 0#
So we are given a history file from a browser. This is in a SQLite database format so I will open it up with my SQLite data viewer.
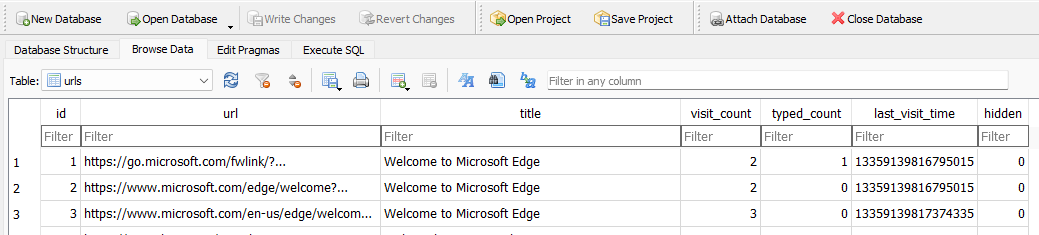
I am looking at the table called urls for most of the parts.
Part 1#
We are looking for a download so let's search for the word download.
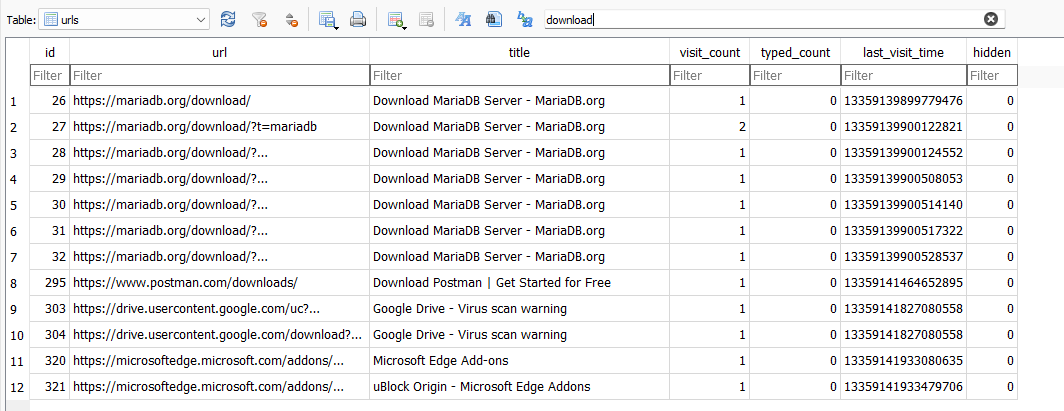
One entry catches my eye because in the title we see virus. Using the URL as the flag we get https://drive.usercontent.google.com/download?id=1BfPZslNaHvz3olaV8_3I6ppA_IbdlHLr&export=download
Part 2#
We are now looking for downloads so let's switch to the downloads table and see if we can find a quote.
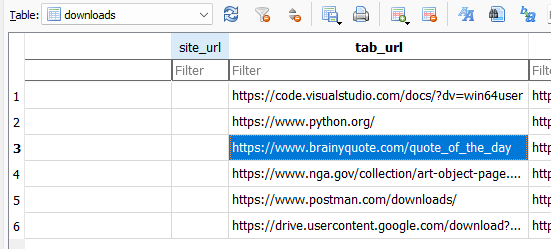
We see a quote of the day site, so now let's look at the downloads_url_chains table to see if we can get a full URL.
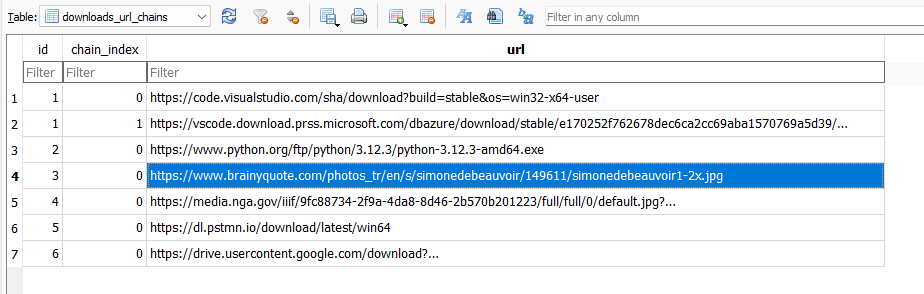
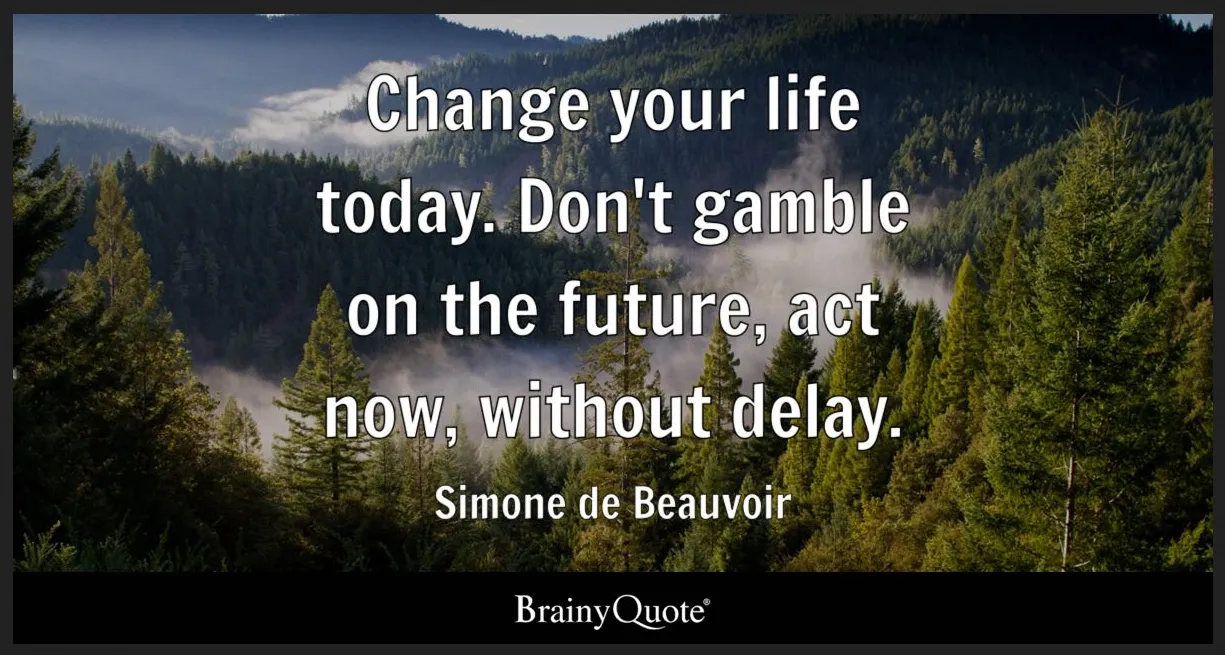
Putting that URL into our browser we see the quote.
Part 3#
We are now looking for flights so we are back in the urls table searching for flights.
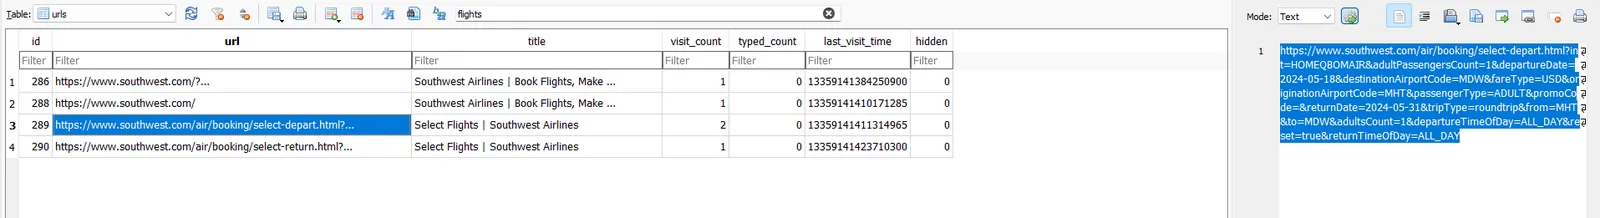
We see a Southwest page with a to and from in the URL request.
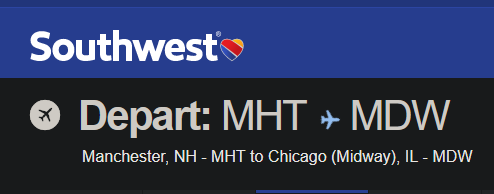
Checking it out shows us the state: New Hampshire
Part 4#
Searching for weather in the urls table.
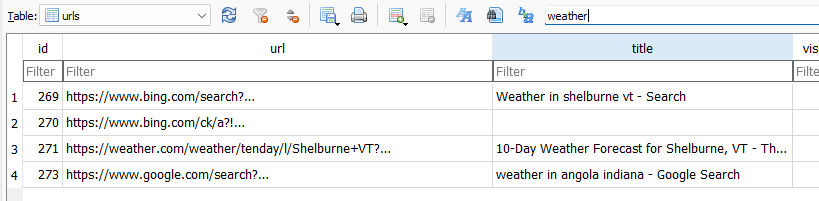
This shows us the city right in the title: Shelburne
Part 5#
Searching for GitHub.
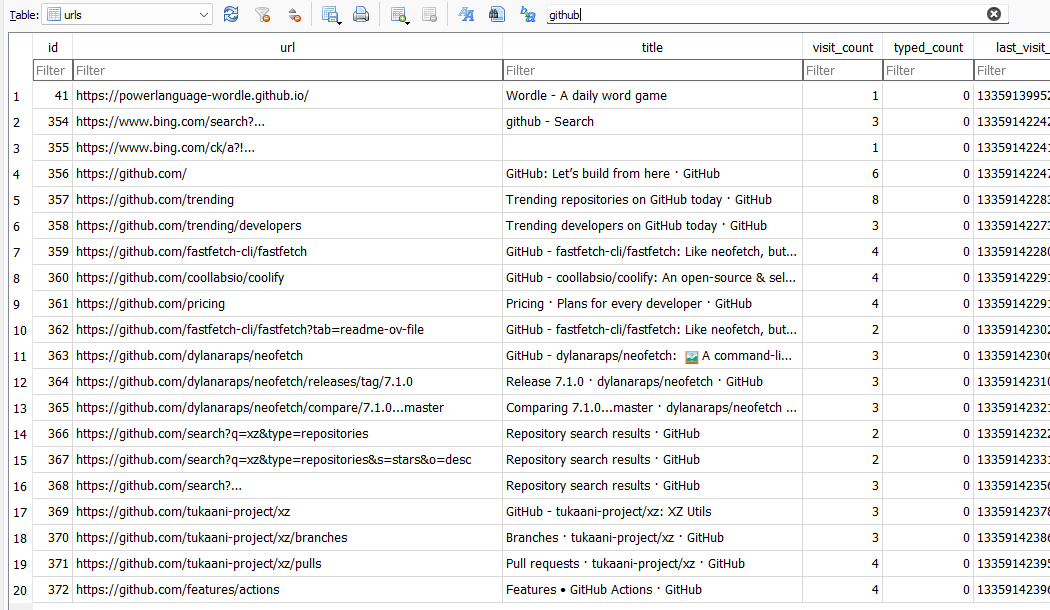
On this list the xz repo stands out to me since I know they had a big news piece. Looking up the associated CVE turns out to be the flag.
Part 6#
This one again we are going to search for the title.
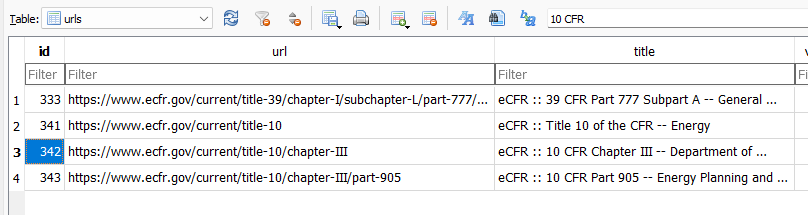
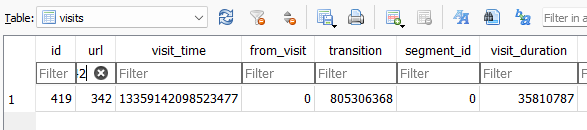
Taking note of the id we can look it up in the visits table, putting the id in for url.
Part 7#
We will search for art.
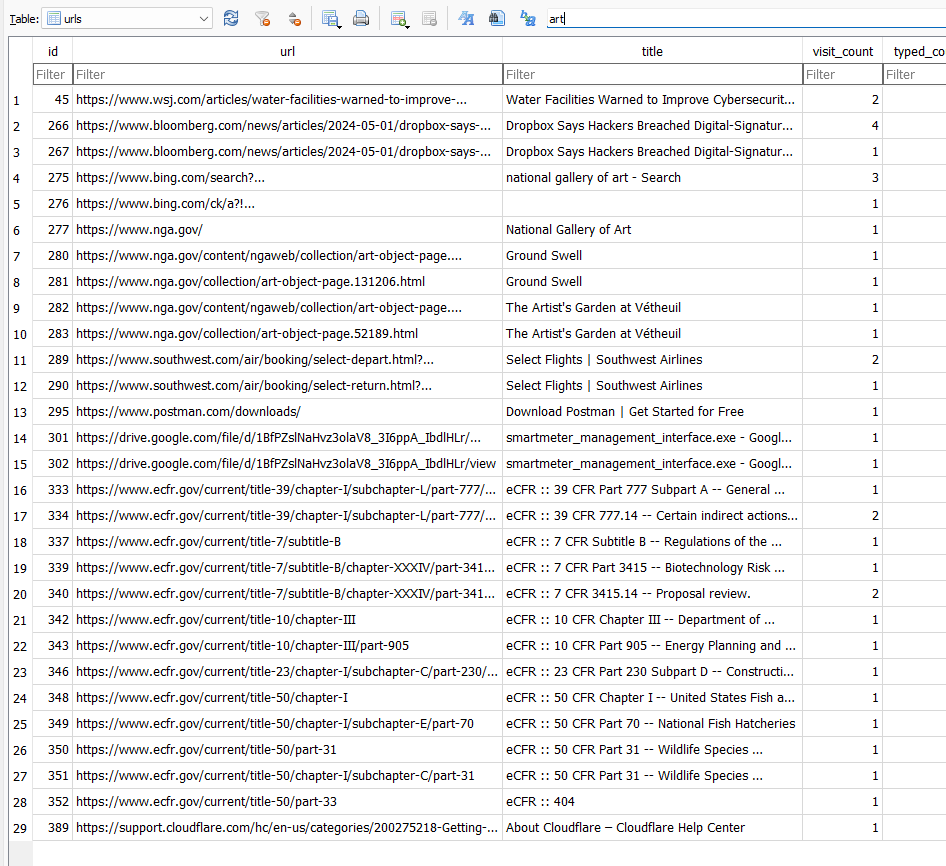
I notice one gov site stands out: the National Gallery of Art.
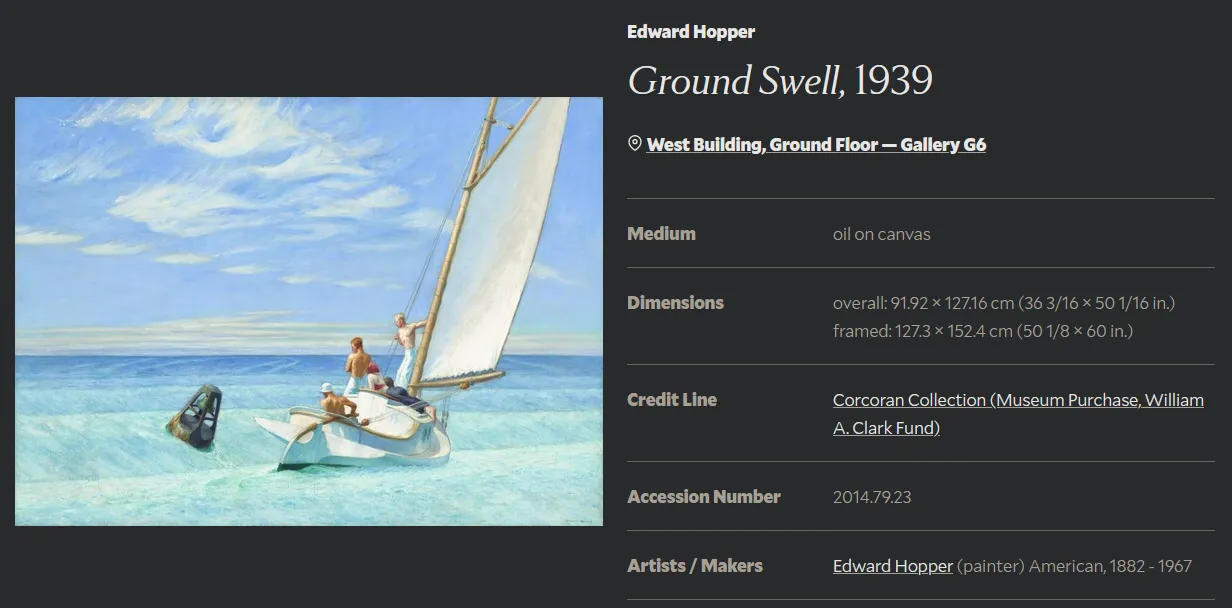
Going to the URL of the painting that wasn't in the downloads table gives us the last name.
Anomaly 12-15: While My WAF Gently Weeps#
Preface#
I am loading these logs into Excel, but you can use any Snort log tool of your choosing.
Anomaly 12#
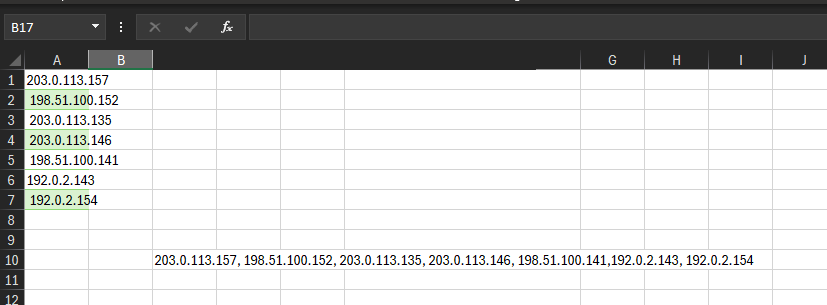
One of the columns has this interesting alert attached to it. Sorting by that reveals a couple of IP addresses.
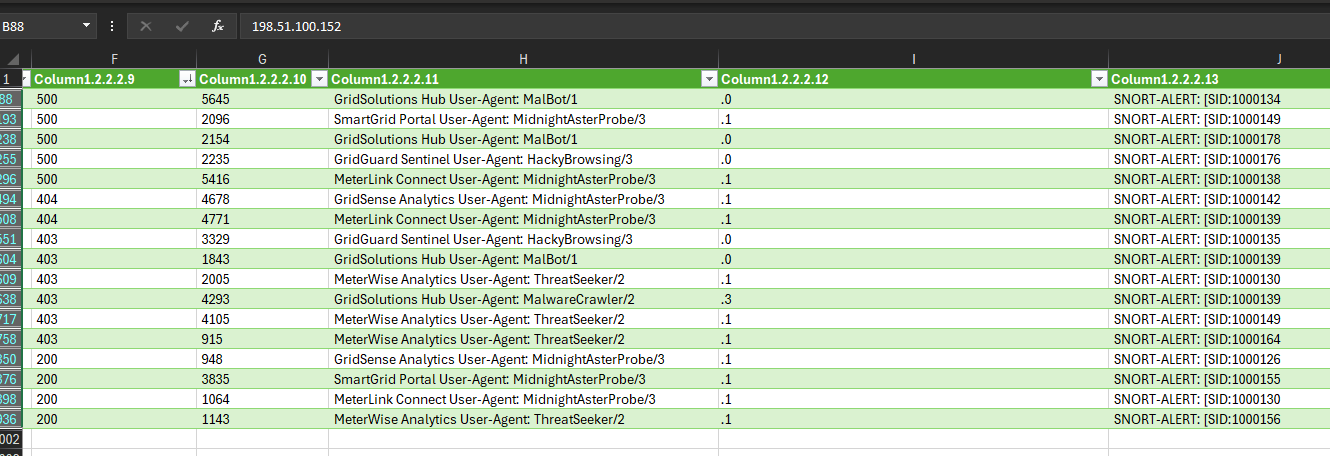
Sorting and removing duplicates plus combining leaves me with
Anomaly 13#
So we know the return status was a 200, so let's sort by that first. Then we see that it is using a site called MeterWise Analytics; let's try filtering that down.
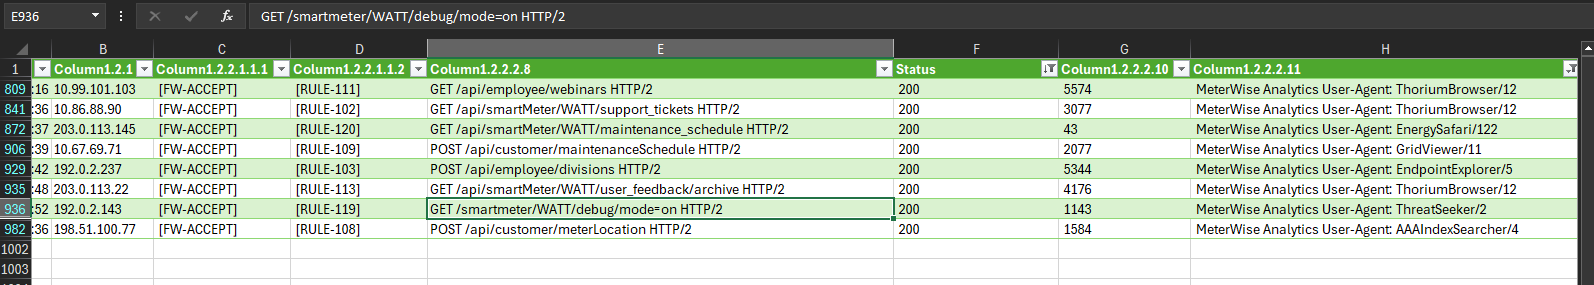
In my column I filter for MeterWise Analytics and see a few options, but one stands out. Having to re-add the one to the user agent gets us the flag.
Anomaly 14#
So we need to filter based on SQL injection, so I am looking for the word OR in the URI.
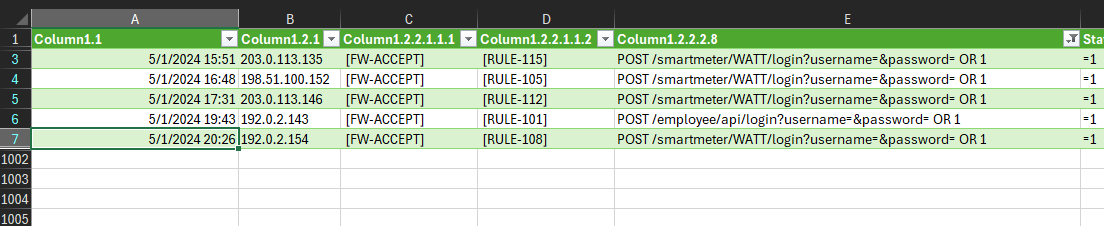
There is the latest one. In Excel I had to put it in the other time format.
Anomaly 15#
We are looking for path traversal, so we need to filter based on ../

One line doesn't have a Snort alert attached to it.
Anomaly 17: Ste-what-graphy v2#
After opening the email in Thunderbird and extracting the attachment into the tools folder:
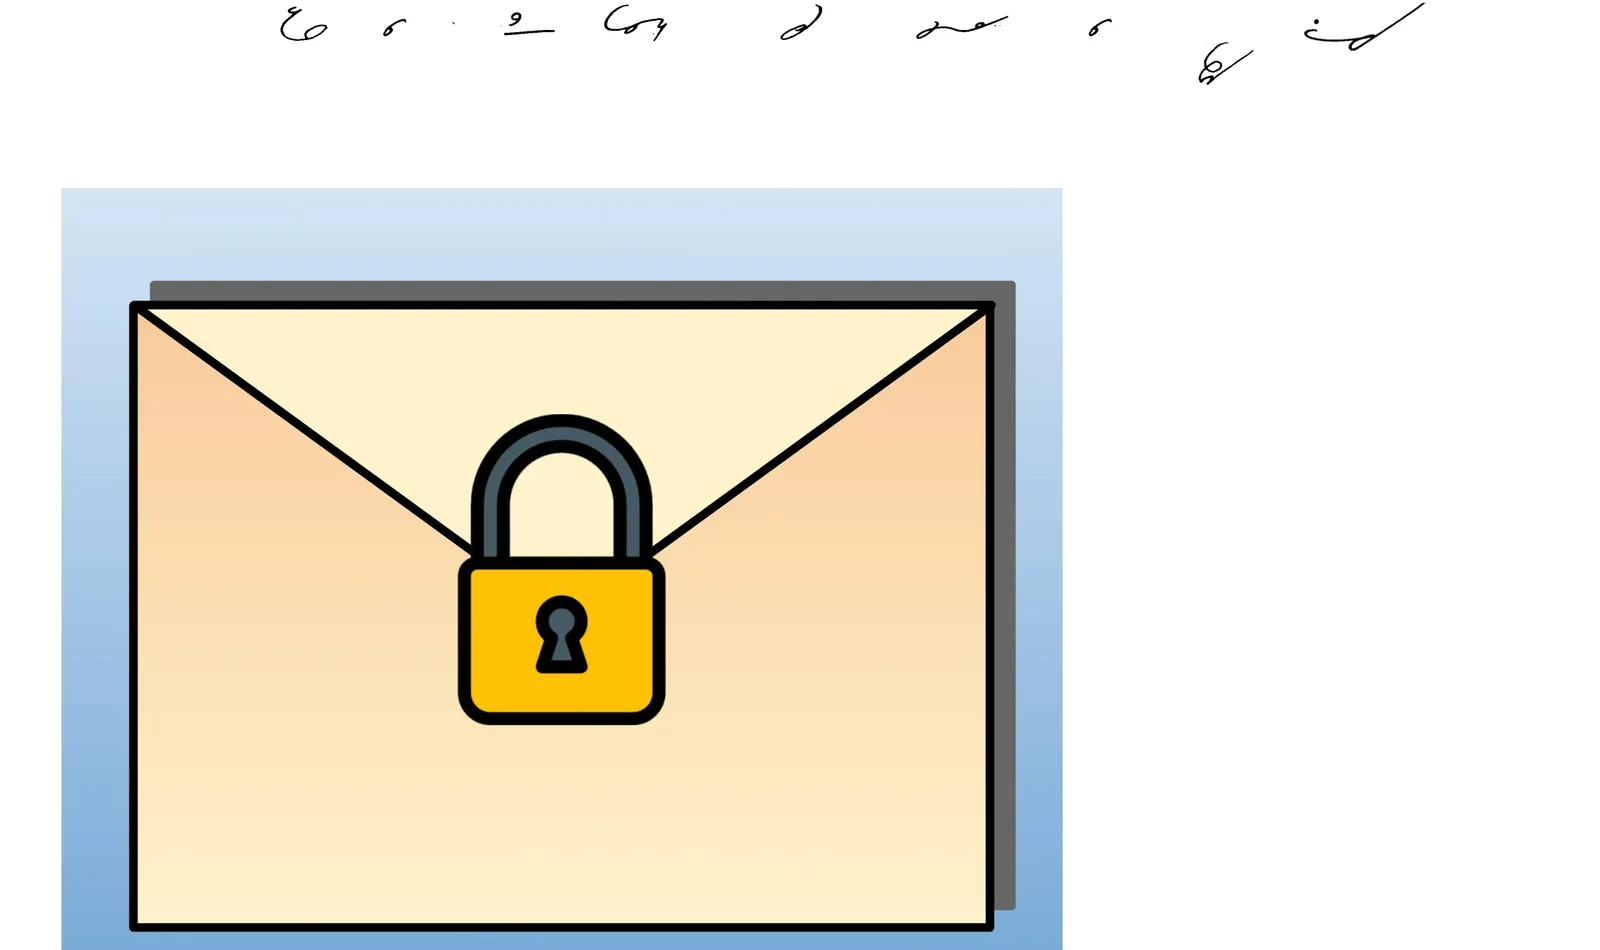
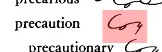
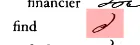
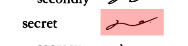
We see some shorthand and a script that claims to be able to read it. Taking a ss of the image and running it through the script will pop a window with potential matches. I had to change the threshold to .8 to not keep getting false positives.
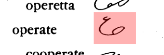
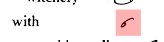
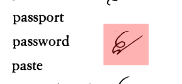
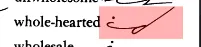
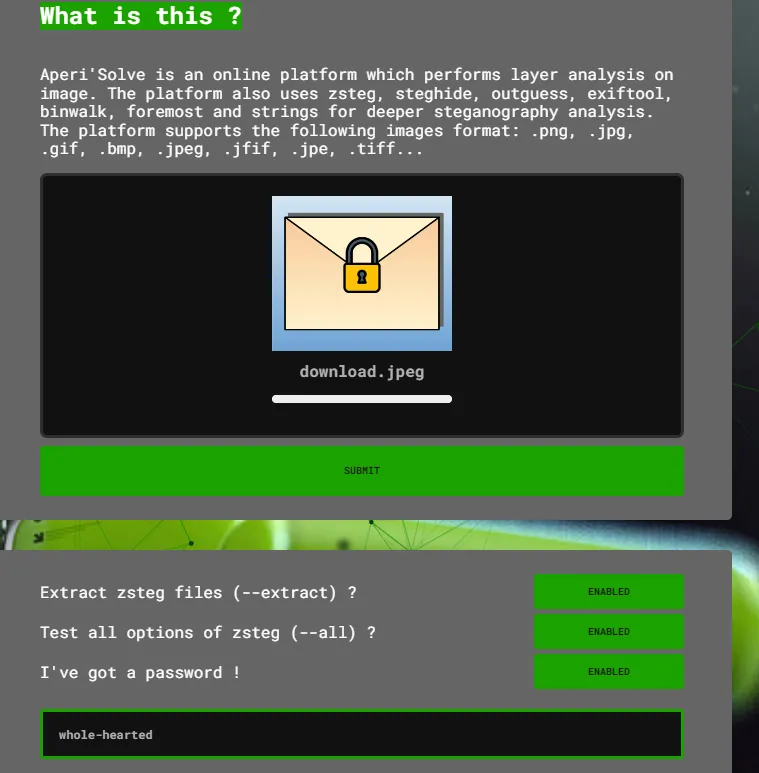
Putting the image into AperiSolve with the password:
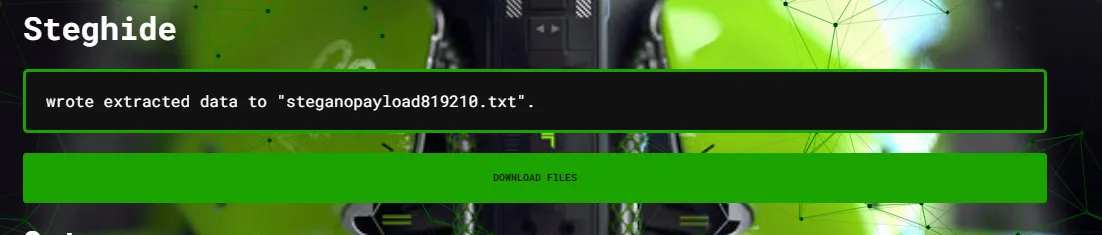
Steghide finds the data and inside is the flag.
Oversee and Govern#
Anomaly 29: Trivia 01#
Which of the following is a technique used in post-exploitation to maintain persistent access to a compromised system without relying on traditional backdoors or implants?
- c) Scheduled task creation - This is correct because it is not something traditional and has to be created by you
- a) Kernel patching - This is incorrect because it would rely on a traditional backdoor
- b) Rootkit installation - This is a traditional method
- d) DLL hijacking - Not known to create persistence
Anomaly 16: COn365nt is Key#
Request 1#
Pass everything Approved
Request 2#
Since this app wants to sign in and when googling I can't find anything about conditional access, it fails DENIED:7
Request 3#
This request wants the permission Read and write all groups which is in the ban list BLOCK:4
Request 4#
This request is not an appropriate type because of a separate email sync DENIED:2
Request 5#
I cannot seem to find its app ID in the system or Google DENIED:3
Request 6#
Since this app wants to read full profiles which can contain data subject to breach notification laws, it fails nine BLOCKED:9
Energy#
Anomaly 39: Trivia 11#
The Department of Energy supports advancements in sustainable transportation. Which of the following is NOT a focus area?
- a. Electric vehicle (EV) infrastructure
- b. Biofuel production
- c. Hydrogen fuel cells
- d. Lead-acid battery research for EVs - We are trying new stuff
Anomaly 40: Trivia 12#
Which U.S. agency launched the "Building a Better Grid" initiative to expand and modernize the nation's electric grid?
- a. Environmental Protection Agency (EPA)
- b. Department of Energy (DOE) - https://www.energy.gov/gdo/building-better-grid-initiative
- c. Federal Energy Regulatory Commission (FERC)
- d. Department of Defense (DOD)
Anomaly 41: Trivia 13#
Which innovative technology was the Department of Energy exploring to enhance grid resilience against cyber-attacks in 2023 according to their GMI calls?
- a. Blockchain technology
- b. Quantum encryption communications - Link to energy.gov report
- c. AI threat detection systems
- d. Satellite grid monitoring
Anomaly 42: Trivia 14#
What should be the primary objective of a risk management strategy? CISM
- a. Determine the organization's risk appetite. - This is just being lazy
- b. Identify credible risks and transfer them to an external party. - We should not just give away all the risk
- c. Identify credible risks and reduce them to an acceptable level.
- d. Eliminate credible risks. - We can never eliminate risks
Anomaly 48: Trivia 20#
Based on the 2023 U.S. Energy Information Administration, this was the leading renewable energy source.
- a. Solar
- b. Hydropower
- c. Wind - Link
- d. Geothermal
Investigate#
Anomaly 49: Knock Knock…Who’s There?#
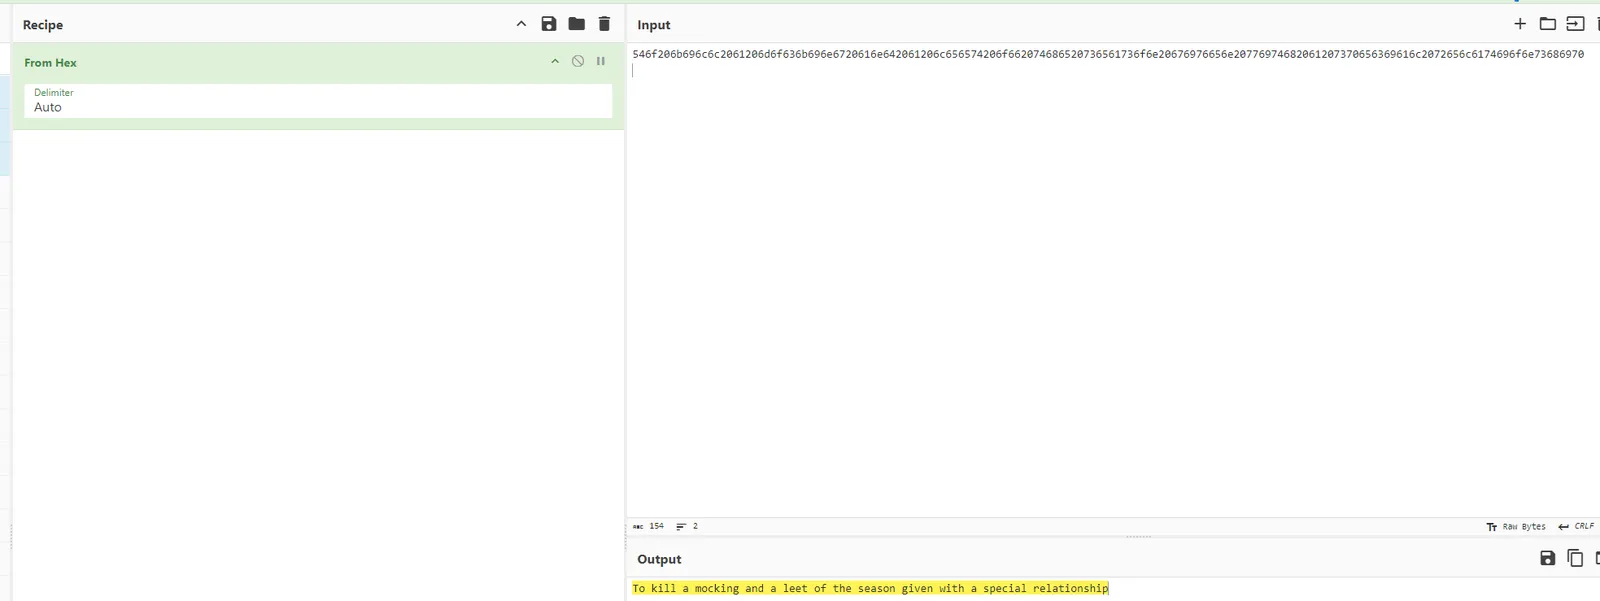
We have a list of encoded text in Base64 and hex; I will convert each back into ASCII.

Anomaly 50: Sloggin through these logins#
Looking at the log file we notice James's account having many incorrect creds: James